Explainer
SecurityNewsExplainer
CVE-2026-98432: a Linux TCP use-after-free in IP options
A critical Linux kernel race in the TCP handshake, fixed in stable kernels: what the bug is, why 'only MPTCP' misleads, how to patch and mitigate.
SecurityHow-toExplainer
Least privilege for AI agents and MCP servers, in practice
Give an AI agent wide room to work and narrow doors to the outside: scopes, sandboxes, MCP tokens and the audit trail a team gets in return.
SecurityNewsExplainer
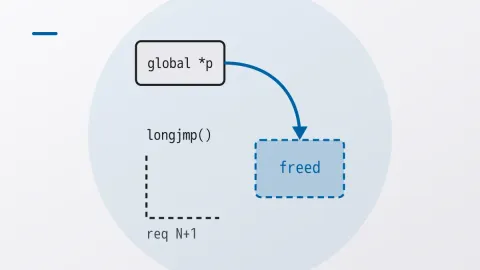
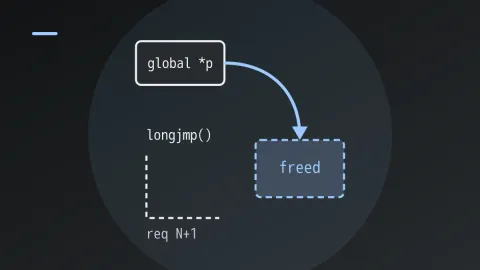
PHP2Shell: when PHP's error exit leaves a mess behind
Two critical PHP RCEs patched on 21 Oct 2026: how longjmp() bailouts leave stale memory behind, how to check your version, and what is unconfirmed.
SecurityExplainer
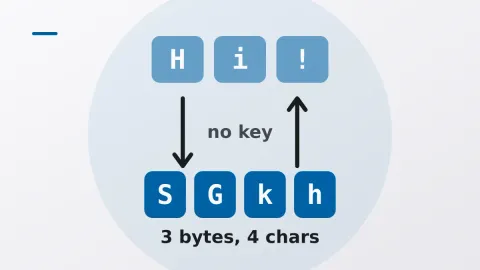
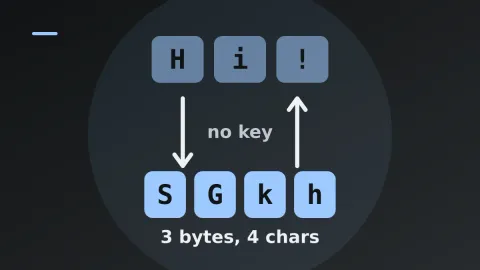
Base64 is encoding, not encryption
A Base64 value in your config is your password in another alphabet. What Base64 is for, where it gets mistaken for encryption, and how to spot it.
ExplainerHow-to
CIDR, the netmask and the router's longest match
Prefix lengths, longest-prefix match, subnet and broadcast arithmetic, why /31 and /32 are special, and the planning mistakes that bite later.
SecurityExplainer
Why length beats composition rules in passwords
Entropy, offline cracking speeds per hash, why passphrases work, what strength meters can't know, and what NIST SP 800-63B really says.
SecurityExplainer
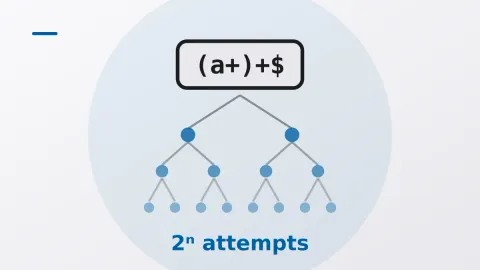
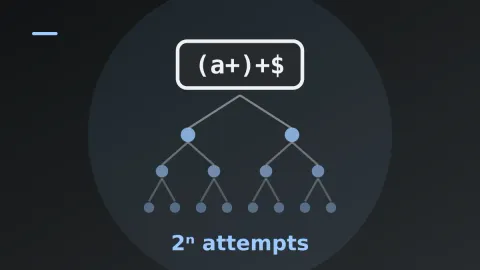
How regex engines backtrack, and what regex can't parse
How backtracking regex engines work, why ReDoS happens (Symfony's Cache-Control bug as a case), what RE2 gives up, and why regex can't parse HTML.
ExplainerPerformanceSecurity
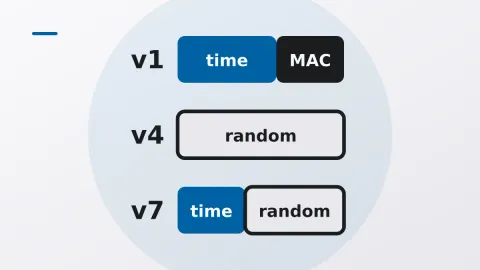
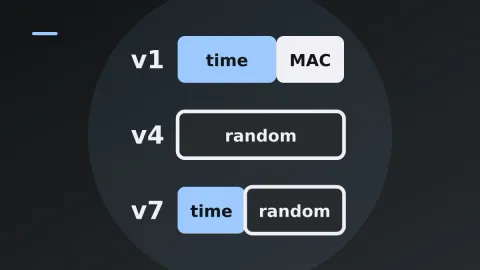
UUID v1, v4 and v7: what leaks, what collides, what scales
What UUID v1, v4 and v7 leak or guarantee, the birthday-bound maths for v4 collisions, and why time-ordered v7 keys keep database indexes fast.
ExplainerHow-to
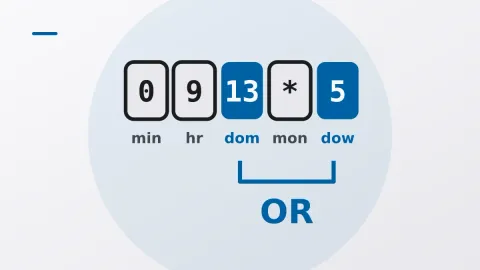
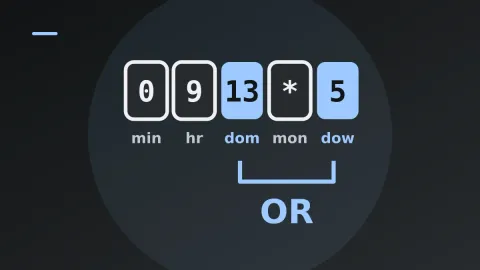
What cron can and cannot do (and how to test it)
Cron's day-of-month OR day-of-week rule, missing seconds, DST gaps and repeats, missed runs, and how to test a schedule before it bites you.
SecurityExplainer
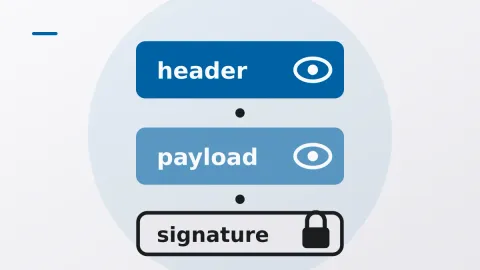
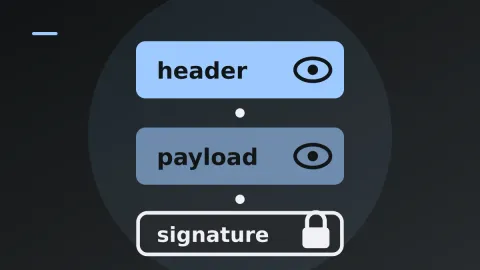
A JWT is signed, not secret
Anyone can read a JWT payload. What the signature does prove, what it doesn't, and the mistakes that turn a token into a vulnerability.